
One Download. Hundreds of Frameworks. No Cost.
The SCF download is not just a controls list. It is a complete GRC toolkit built by volunteer cybersecurity and data privacy experts that is released free under Creative Commons licensing.
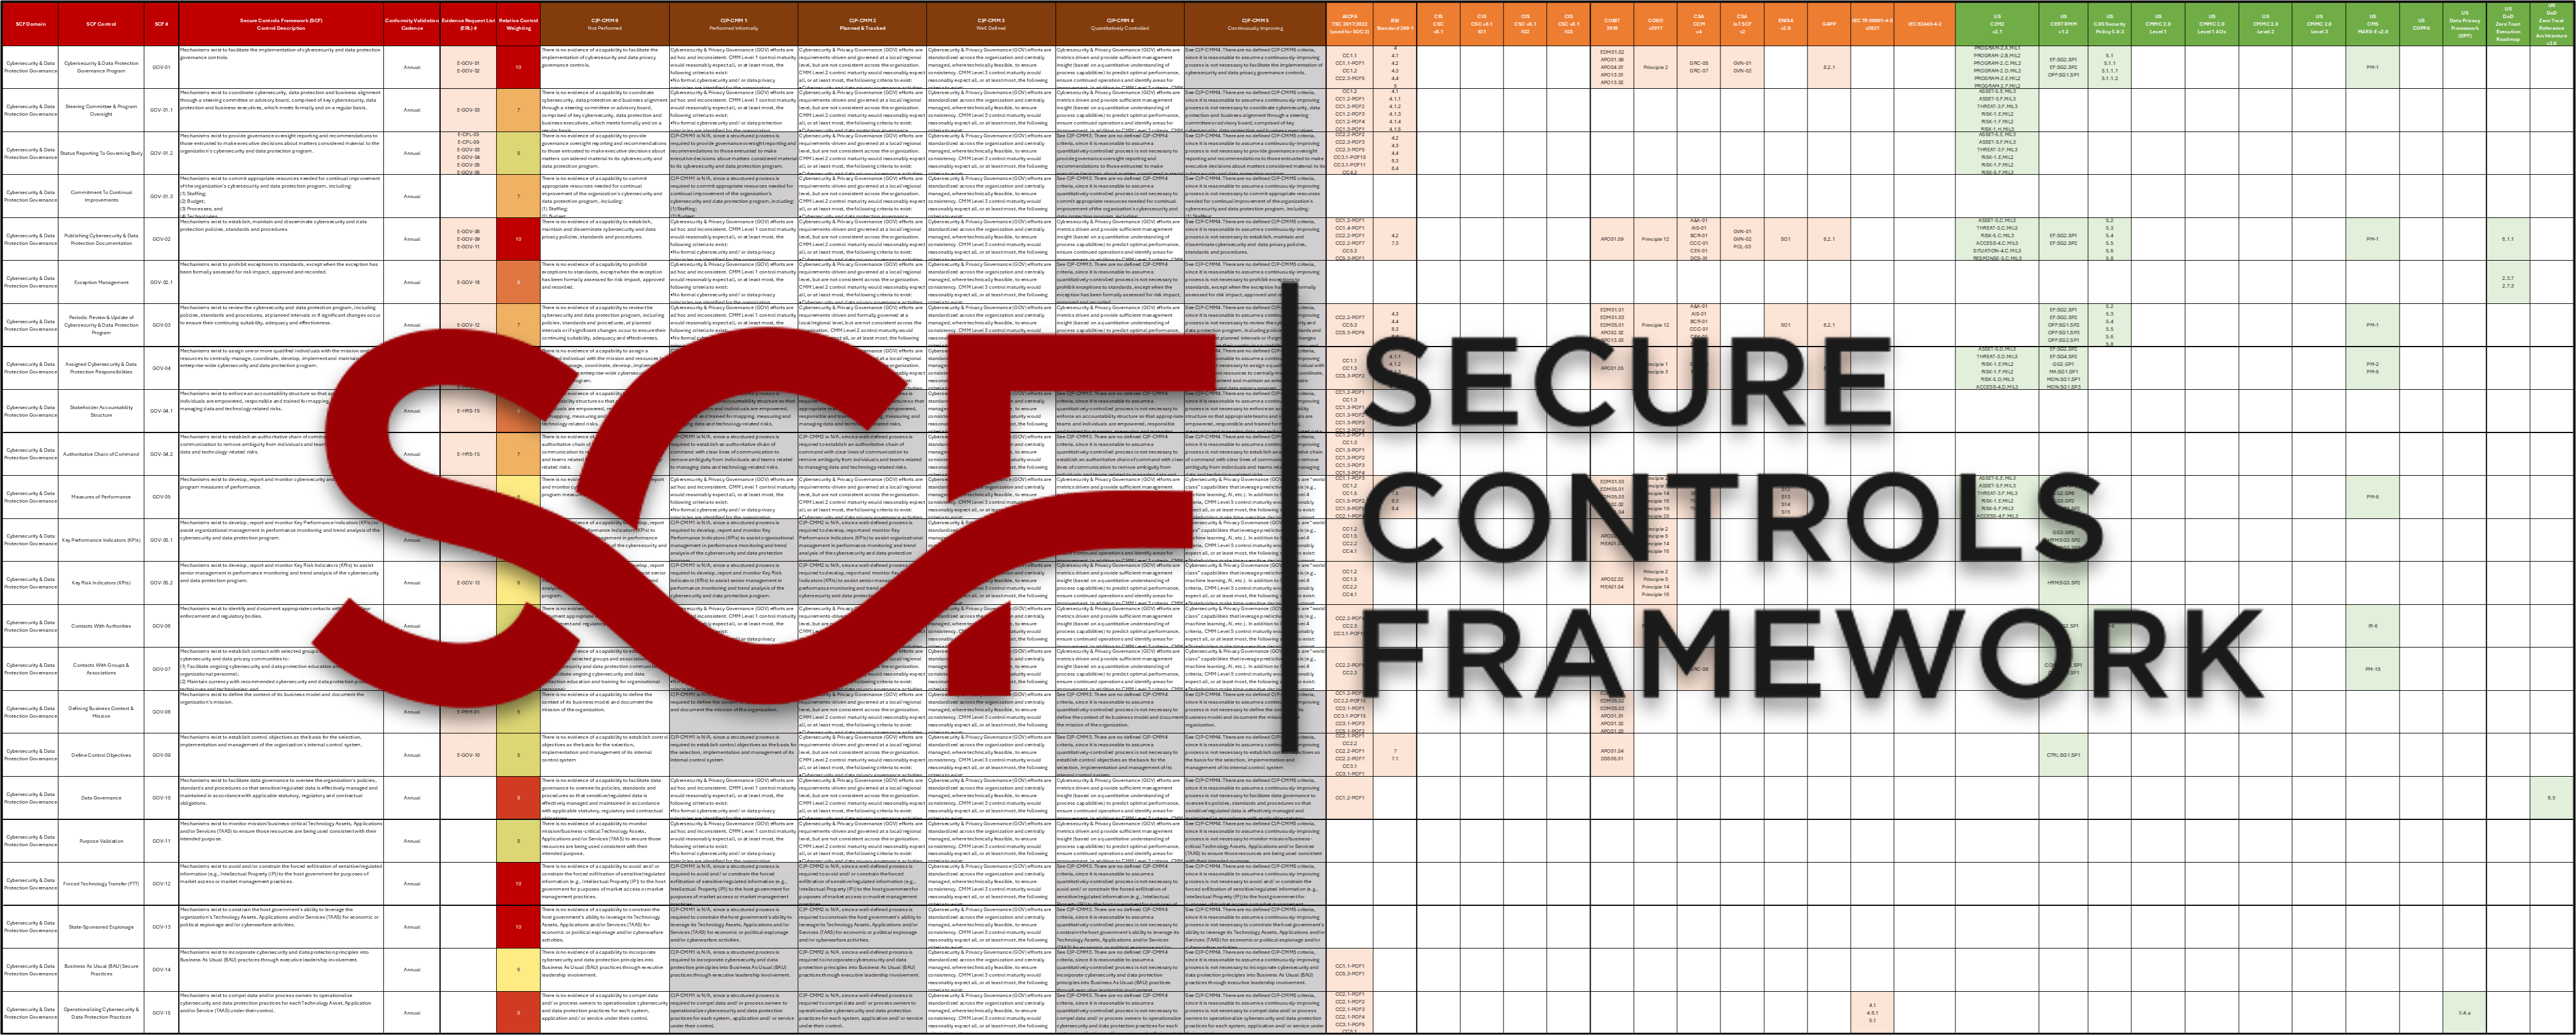
A single download gives you the full 1,500+ control catalog, all 200+ framework mapping tabs, SCR-CMM maturity criteria for every control, proposed risk weightings, MCR/DSR classification, risk and threat catalog crosswalks, and Assessment Objective (AO) guidance. Everything needed to build and assess a cybersecurity program from any starting point.
The SCF is the basis for your organization's Living Control Set (LCS). The SCF is updated on a quarterly basis to include changes whenever a new law is enacted, a framework releases a new version, or an emerging threat demands new controls.
Volunteer-Driven. Creative Commons Licensed. All SCF content is developed by volunteer cybersecurity practitioners, including CISOs, auditors, GRC specialists, privacy experts, and engineers, and released at no cost under Creative Commons Attribution-NoDerivatives 4.0 International.
Download the SCF
Fill out the short form to access the full SCF download. No account required, just basic contact information so we can keep you informed about new releases.
We use this contact information to notify SCF users of changes, such as new releases.
Access the Full SCF Download
Prefer To Skip The Form?
The full SCF is always available on GitHub with no registration or login required. The form is optional but helps us understand adoption and improve the framework.
What Do You Get When You Download The SCF?
The SCF is a comprehensive document that has 34 domains, contrains over 1,500 controls, and maps to over 200 laws, regulations, and frameworks. When you download it, beyond these, you will also get the following:
SCF Spreadsheet
The primary SCF download. The full control catalog with all framework mapping tabs, maturity criteria, risk catalog, and threat catalog in a single multi-tab workbook.
NIST OSCAL JSON
Machine-readable Open Security Controls Assessment Language (OSCAL), the NIST standard for structured control data, enabling automated compliance workflows and OSCAL-native tool integration. SCFConnect maintains the OSCAL version of the SCF.
Inside Every Download
Alongside the standard spreadsheet, the SCF comes with the following:
Control Catalog With 1,500+ Controls
SCR-CMM Maturity Criteria
MCR / DSR Classification
Threat Catalog Crosswalk
Framework Mappings: 200+ Laws & Frameworks
Proposed Control Weighting
Risk Catalog Crosswalk
Assessment Objectives (AOs)
Free to use under the Creative Commons Attribution-NoDerivatives 4.0 International license. Updated on a quarterly basis.
What Can You Do With The SCF In Your First Hour?
Open the spreadsheet and find the laws, regulations and frameworks that apply to you. Filter the SCF controls mapped to them; that filtered list is your first common control set. Then score a few high-risk controls with the SCR-CMM maturity criteria to see where you stand.
What's Included In The SCF Download
The SCF download is a complete GRC toolkit, far more than a control catalog. Here is everything inside every download.
Framework Mappings: 200+ Laws & Frameworks
Every SCF control is mapped to all applicable laws, regulations, and industry frameworks using the transparent NIST IR 8477 STRM methodology. Directional mappings show whether SCF covers, partially covers, or exceeds each external requirement.
SCR-CMM Maturity Criteria
Six-levels of maturity criteria (Ad Hoc through AI-driven processes) for every SCF control, built directly into the spreadsheet so organizations can immediately score their current control maturity.
Proposed Control Weighting
Risk-based weighting for every control, essential for prioritizing remediation, allocating resources, and producing defensible risk scores for board-level reporting.
MCR / DSR Classification
Every control is classified as a Minimum Compliance Requirement (MCR), meaning externally mandated, or a Discretionary Security Requirement (DSR), meaning risk-based and internally driven.
Risk Catalog Crosswalk
Risks are mapped to the SCF controls that mitigate them, enabling risk-informed control selection and residual risk analysis when controls are partially implemented.
Threat Catalog Crosswalk
Threats are mapped to the SCF controls that address them, enabling threat-informed defense and right-sizing security investment based on the actual threat landscape.
Assessment Objectives (AOs)
Examiner guidance per control provides the criteria used to evaluate whether a control is effectively implemented. This removes ambiguity from both self-assessments and third-party audits.
Using the SCF for SOC 2 and ISO 27001
Many teams download the SCF to run SOC 2 and ISO 27001 from one control set. Filter the spreadsheet to the controls mapped to the Trust Services Criteria and to ISO 27001, assign one owner and one evidence artifact per control, and reuse that evidence for both engagements. When you want a third-party certification against SCF controls, see the SCR Conformity Assessment Program.
Import Into Any GRC Platform
The SCF is utilized by many leading GRC platforms worldwide. Import the full 1,500+ control catalog with all mappings via .CSV or JSON (NIST OSCAL formatted) in minutes, not months.
Unlike proprietary frameworks that lock you into a single vendor ecosystem, the SCF uses open, standardized formats. Your control data is yours, portable, exportable, and not dependent on any single tool vendor.
Get Connected & Stay Involved
The SCF is more than a download. It is a living community of cybersecurity and GRC practitioners. Get the latest version on GitHub, ask questions in Discord, or support the mission with a donation.
Download on GitHub
The SCF is hosted on GitHub, the canonical source for all downloads. No account required. Watch the repository to be automatically notified when a new version of the Living Control Set is published.
Join the Discord
Connect with thousands of cybersecurity and GRC practitioners in the SCF community Discord. Ask questions, share your experience, discuss emerging regulations, and stay up to date on releases.
Support the SCF
The SCF is built and maintained entirely by volunteers and funded through donations. If the SCF has saved your organization time, money, or compliance headaches, please consider donating.
